Office printers leak data
A confidential audit reveals that outdated settings on multifunction devices expose sensitive information in agencies nationwide.
By Lauren Foster ·
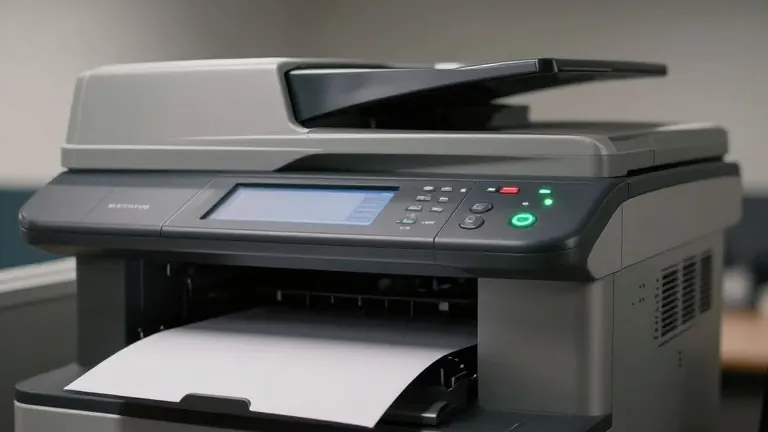
Hackers can access sensitive documents through a simple configuration error on office printers. A confidential audit of several agencies found that these devices often hold data well beyond the immediate job of copying or scanning.
Modern multifunction devices frequently include hard drives and firmware. The audit showed that many of these units retain scan histories, address books, and network settings. Some machines still use default passwords that have never been changed.
The investigation identified potential problems across the country. The risk is not limited to private businesses. Doctors, schools, and police departments face exposure if their equipment remains on the local network with weak protections.
The core issue is the assumption that a printer is a passive tool. It is not. It is a connected computer that stores information. If the device is not configured securely, it becomes an entry point for attackers looking for specific files or credentials.
The audit suggests that a change in settings could mitigate the risk. Agencies must review how their devices handle data storage and network access. This is not a matter of the hardware failing, but of the software configuration being left on its initial state.
The findings align with a broader trend in corporate security. As offices move toward remote work and cloud storage, the physical devices in the room are often overlooked. The printer in the corner is a data point that can compromise the whole system.
Experts advise checking the default credentials and disabling unused network features. The audit did not name the specific agencies involved. It provided a general framework for the types of vulnerabilities found in the review.