Unchanged Default Passwords on Office Printers Leave Agencies Vulnerable to Hackers
A confidential audit reveals that outdated settings on multifunction devices are exposing sensitive data in government and medical offices across the country.
By Lauren Foster ·
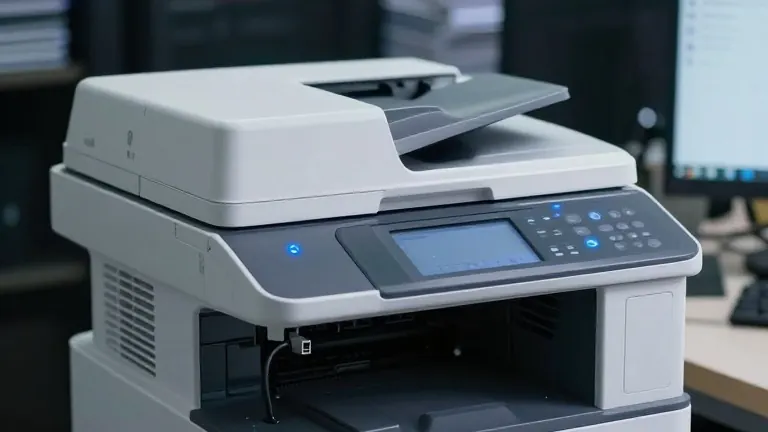
Office printers are often overlooked targets in cybersecurity, yet a recent investigation suggests they pose a tangible risk to sensitive data. A confidential audit of machines at several agencies found that outdated settings could allow hackers easy access to internal networks.
The audit, reviewed by InvestigateTV, identified specific weaknesses in how modern multifunction devices are configured. These machines, which hum in corners of offices nationwide, do more than copy paper. Depending on the model, they store documents, scan histories, address books, and network settings. Some units even contain hard drives and firmware that retain information long after a job is complete.
A primary concern is the use of default passwords. Many devices ship with preset credentials that administrators often fail to change. This creates a direct path for unauthorized users to view or steal data. The audit indicated that these vulnerabilities exist in settings that have not been updated for years.
The findings place pressure on organizations to reevaluate how they manage peripheral hardware. Doctors, schools, and police departments were among the types of entities mentioned as being at risk. The report suggests that the physical location of these printers, often in shared spaces, compounds the digital threat.
While the audit focused on specific agencies, the technology is common across many sectors. The devices involved range from simple scanners to complex multifunction units. The core issue remains the gap between the capabilities of the hardware and the security configurations applied to it.
The report did not name every agency audited, but it provided a clear framework for identifying at-risk equipment. The presence of a hard drive or a stored address book without encryption was cited as a key indicator. Administrators are urged to check their network settings and change any factory-set passwords immediately.
This finding adds to a growing list of hardware vulnerabilities in modern workplaces. The data collected from these printers can include personal identifiers and internal communications. The audit serves as a warning that security efforts must extend beyond servers and laptops to include the devices that process physical paperwork.